In software testing, understanding both the internal structure and external behavior of an application is crucial for delivering quality results. This is where Grey Box Testing becomes especially valuable. It bridges the gap between white box and black box testing, providing a balanced approach to identifying defects.
In this blog, we’ll explore what grey box testing is, when to use it, why it matters, and how it enhances the software development lifecycle.
What is Grey Box Testing?
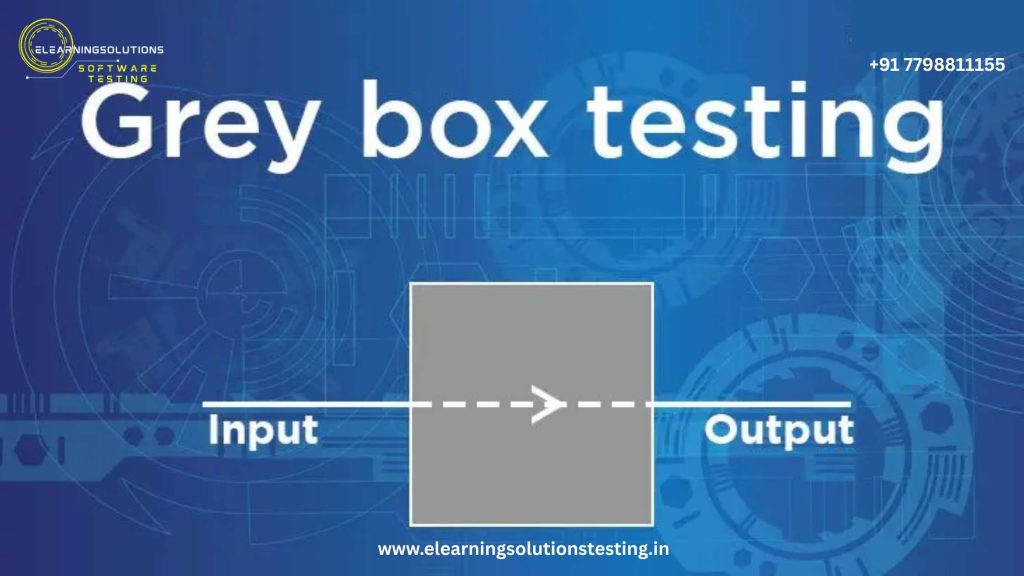
Grey box testing is a hybrid testing method that combines elements of both white box testing (code-level knowledge) and black box testing (external behavior testing). The tester has partial knowledge of the internal structure of the system, typically at the architectural or database level, but not complete access to the source code.
This method allows testers to design more informed and efficient test cases, especially in scenarios where both functionality and internal operations need to be validated.
Why Use Grey Box Testing?
Grey box testing provides a balanced perspective. It leverages the strengths of both black box and white box techniques, allowing testers to:
- Test from a user’s perspective with technical insight
- Identify security vulnerabilities
- Validate data flow and database integrity
- Verify the interaction between different modules or layers
When Should You Use Grey Box Testing?
- During Integration Testing
When different modules or services interact, grey box testing ensures data flows correctly and internal APIs function properly. - In Web Applications
Testers can check form submissions, cookie handling, session management, and server-side processes with partial backend knowledge. - For Security Testing
Grey box testers can simulate potential attacks with partial information, helping identify hidden vulnerabilities. - Testing APIs
When you know the structure of the request and response, but not the internal code, grey box testing becomes ideal. - Regression Testing
When changes are made to internal logic, grey box testing ensures that they haven’t broken existing functionality.
How is Grey Box Testing Performed?
Grey box testing involves:
- Reviewing available design documents, architecture diagrams, and database schemas
- Creating test cases based on internal knowledge and expected output
- Performing test scenarios that cover both front-end functionality and back-end processes
- Analyzing logs, server responses, and database changes to detect issues
Real-World Example of Grey Box Testing
Scenario: Testing an E-Commerce Checkout System
A tester is given access to the database schema and the workflow of the checkout process, but not the actual code.
They test:
- Whether the correct tax is applied based on user location
- If discount coupons are calculated and recorded properly in the backend
- Whether stock updates in the inventory database after successful payment
- Session management during the checkout process
This approach helps validate the business logic while also checking for functional correctness.
Advantages of Grey Box Testing
- Offers greater test coverage than black box testing
- Requires less time and resources than full white box testing
- Uncovers internal issues without needing full access to code
- Effective for security, integration, and system testing
- Allows early bug detection by understanding architecture
Limitations of Grey Box Testing
- Partial code knowledge can lead to incomplete analysis
- May miss low-level bugs that full white box testing can detect
- Effectiveness depends on tester’s skill and available documentation
- Not ideal for pure functionality testing from the end-user’s perspective
Grey Box vs. White Box vs. Black Box Testing
| Feature | White Box | Grey Box | Black Box |
|---|---|---|---|
| Code Knowledge | Full | Partial | None |
| Perspective | Developer | Tester + Dev | End User |
| Test Focus | Logic + Structure | Logic + Behavior | Functionality |
| Ideal For | Unit Testing | Integration, Security | UI/UX Testing |
Conclusion
Grey box testing is a powerful and flexible testing method, especially in modern development environments where understanding both the internal structure and external behavior is critical. It is best suited for integration, security, and system-level testing where testers benefit from partial knowledge of the application.
YOU MAY BE INTERESTED IN
The Art of Software Testing: Beyond the Basics
Automation testing course in Pune
Automation testing in selenium
Mastering Software Testing: A Comprehensive Syllabus
Frequently Asked Questions
What is grey box testing and how does it differ from other testing methods?
Grey box testing is a software testing method that combines elements of black box and white box testing, where the tester has some knowledge of the internal workings of the application, but not full access to the code. This approach allows for more efficient testing than black box testing, while also providing a more realistic testing environment than white box testing. By using grey box testing, testers can identify issues that may not be apparent through other testing methods.
When should I use grey box testing in my software development process?
Grey box testing is particularly useful during the integration and system testing phases, where the focus is on ensuring that different components of the application work together seamlessly. It is also effective in identifying security vulnerabilities and performance issues that may not be apparent through other testing methods. By incorporating grey box testing into your development process, you can improve the overall quality and reliability of your software.
What are the benefits of using grey box testing in my software development project?
The benefits of grey box testing include improved test efficiency, increased test coverage, and enhanced defect detection. Grey box testing also allows testers to identify issues that may not be apparent through other testing methods, such as security vulnerabilities and performance issues. By using grey box testing, you can reduce the risk of defects and improve the overall quality of your software.
How does grey box testing differ from penetration testing?
While both grey box testing and penetration testing are used to identify security vulnerabilities, they differ in their approach and scope. Grey box testing is a broader testing method that focuses on identifying defects and issues in the application, including security vulnerabilities, whereas penetration testing is a more focused approach that specifically targets security vulnerabilities. Grey box testing is typically performed by testers who have some knowledge of the application’s internal workings, whereas penetration testing is often performed by external security experts.
What skills and knowledge are required to perform grey box testing effectively?
To perform grey box testing effectively, testers need to have a good understanding of the application’s internal workings, as well as its external interfaces and interactions. They should also have knowledge of testing methodologies, defect detection techniques, and analytical skills to identify and report defects. Additionally, grey box testers should be familiar with the application’s code and architecture, as well as relevant testing tools and technologies.